Policy-Driven Cryptographic Agility & The Sovereign Trust Fabric
The KeyMESH serves as the modular, policy-driven cryptographic routing nervous system of the onePOI.online ecosystem. Traditional computing models hardcode cryptographic libraries directly into client applications, resulting in costly, months-long code refactoring cycles whenever algorithms must be upgraded. KeyMESH inverts this paradigm by completely abstracting mathematical execution from application logic.
To solve the Digital Public Infrastructure (DPI) Trilemma – balancing uncompromising security, hyperscale distribution, and hardware unit economics – KeyMESH deploys a "Fortress and Field" model. Centralised Master Root Keys reside exclusively in high-assurance Tier 1 Cloud HSMs ("The Fortress"), whilst edge POI terminals ("The Field") operate as completely empty vessels regarding static credentials. Ephemeral session keys are injected Just-in-Time (JIT) into hardware enclaves and shredded immediately upon transaction finality.
KeyMESH Runtime Manifest
Multi-Tenant Cryptographic Orchestrator
Commercial Sovereignty & Shared Phygital Infrastructure
In shared commercial environments – such as municipal kiosks, automated teller cash recyclers, and smart retail lockers – physical theft or endpoint tampering presents catastrophic liability. If static master keys reside on-disk, compromising one appliance compromises the entire tenant institution. KeyMESH eradicates this risk by ensuring edge hardware contains zero persistent cryptographic credentials.
As the cryptographic backbone of the Salient FinTech Innovation Set, KeyMESH natively integrates with BIAN v14 bare-metal service domains (Payment Execution, Party Authentication, Cryptographic Services) and real-time payment rails (SEPA Instant, FedNow, RTP, Discover/Pulse). Competing financial and civic institutions share unified physical appliances whilst maintaining absolute, mathematically enforced sovereign isolation.
Zero Edge Key Theft
If an appliance is stolen or drilled, the attacker captures empty silicon with no static credentials.
Zero-Truck-Roll Key Injection
Automates Remote Key Injection (RKI) via TR-34 tunnels without requiring manual field technicians.
Multi-Tenant Key Curtaining
TR-31 usage tags cryptographically prevent Tenant A's software from misusing Tenant B's keys.
Post-Quantum Agility
Hot-swaps classical ECC/RSA for NIST FIPS 203/204 PQC algorithms via simple Agreement DAG updates.
The 4-Stage Industrial Cryptographic Supply Chain
KeyMESH governs the entire lifecycle of cryptographic secrets across edge and cloud infrastructure. From physical entropy harvesting to hardware-bound usage encapsulation, every stage adheres to rigorous international standards.
Entropy Mesh & EaaS
Eliminates edge "entropy starvation" at boot. Centralised Quantum Random Number Generator (QRNG) beacons supply cryptographically certified entropy seeds (NIST SP 800-90B) to initialise appliance cryptographic pools.
Policy Hash Gating
Applications issue abstract intents (e.g. SIGN_CREDENTIAL). KeyMESH evaluates the active Agreement DAG and Policy Hash (PH), dynamically selecting mathematical algorithms based on jurisdiction and threat posture.
XFS4IoT & TR-34 Tunnels
CEN XFS4IoT WebSockets provide OS-agnostic communication with peripherals. Remote Key Loading (TR-34) establishes blind, asymmetric encrypted tunnels from Cloud HSMs directly into peripheral Secure Elements (EPPs).
TR-31 Smart Containers
Keys are encapsulated inside TR-31 (ANSI X9.143) key blocks where usage permissions (OPPs) are cryptographically bound to the ciphertext. Any unauthorised alteration corrupts the MAC and causes immediate hardware rejection.
Structural Separation of Powers: State, Evidence, Flow & Execution
A sovereign digital economy requires more than isolated execution boundaries; it requires an authoritative control plane that substantiatedly proves the Present State (Registrar), the Past Evidence (Notary), and the Cryptographic Flow (KeyMESH), physically enforced within the oneVault MESH execution fabric.
Registrar & KeyMESH Attestation
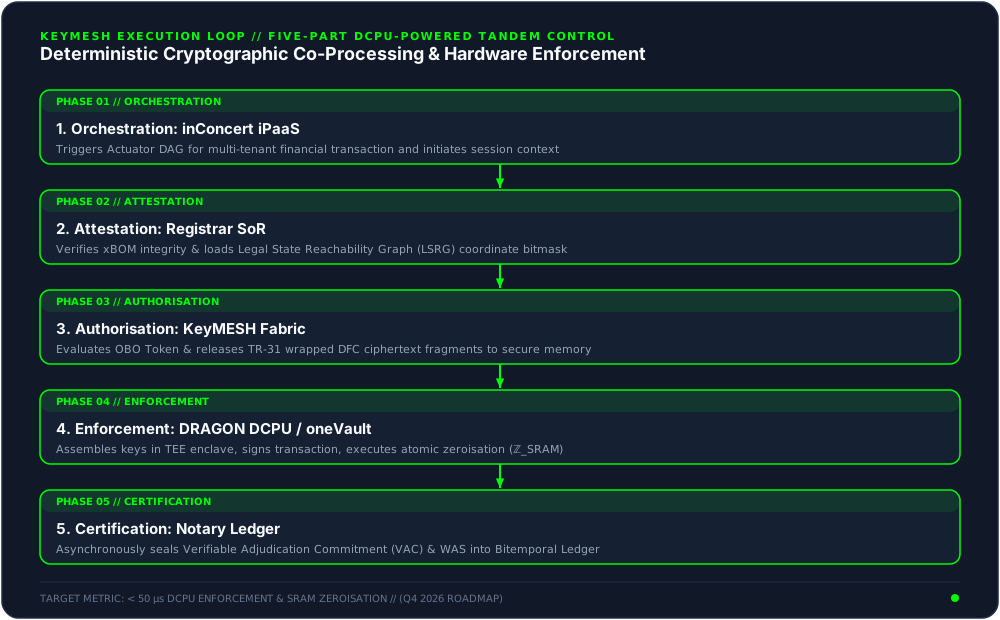
The Registrar performs recursive attestation of node xBOMs against the active Policy Hash (PH). KeyMESH only routes Distributed Fragment Cryptography (DFC) ciphertext payloads after verifying this Attestable Trust Envelope. Atomic Map Update syscalls push revocation state instantly to kernel eBPF filters.
KeyMESH & oneVault MESH Assembly
KeyMESH routes encrypted fragments across isolated network tiers. Full keys are never held on any single server; they are re-assembled strictly inside the hardware TEE "Silicon Apartment" (AMD SEV-SNP / Intel TDX) on the DRAGON DCPU at the exact moment of execution.
oneVault MESH & Notary VACs
As execution concludes, oneVault generates a Verifiable Adjudication Commitment (VAC). The Notary acts as an asynchronous observer, committing the VAC and Wipe Attestation Signature (WAS) to the Bi-Temporal Ledger without adding synchronous latency to line-rate financial flows.
Ecosystem Authoritative Trinity Links
KeyMESH operates in continuous synchronisation with the Registrar for active policy hashing, the Notary for non-repudiation audit trails, and oneVault Mesh for confidential enclave execution.
Next-Gen Cryptography: Post-Quantum Security & Sovereign Keys
Explore how KeyMESH achieves quantum-resilient key management using NIST-standardised lattice-based primitives (ML-KEM / Kyber, ML-DSA / Dilithium) with zero-trust hardware enclave execution.
Deep Technical: Remote Key Loading (TR-34) & Blind Enclave Tunnels
Deep Technical: Remote Key Loading (TR-34) & Blind Enclave Tunnels
Traditional Remote Key Injection (RKI) methods are vulnerable if the host operating system of an edge kiosk is compromised by malware or rootkits. Under the KeyMESH architecture, the host Linux operating system acts merely as an untrusted transport bridge.
Using the ASC X9 TR-34 standard, a dual-asymmetric public key handshake is established between the central Cloud HSM and the physical Secure Element (SE) / Encrypting PIN Pad (EPP). The ephemeral session keys are encrypted with the EPP's factory-fused public key inside the Cloud HSM. When the payload traverses the local appliance bus, the host OS cannot inspect or copy the key material. The key is decrypted exclusively inside the hardware-isolated cryptographic boundary of the peripheral.
Deep Technical: Post-Quantum Hybrid Migration (Kyber & Dilithium)
Deep Technical: Post-Quantum Hybrid Migration (Kyber & Dilithium)
KeyMESH is architected for quantum resilience from first principles. Rather than mandating immediate, brittle "forklift upgrades" of legacy hardware, KeyMESH supports hybrid cryptographic states as codified by NIST FIPS 203 (ML-KEM / Kyber), FIPS 204 (ML-DSA / Dilithium), and FIPS 205 (SLH-DSA / SPHINCS+).
In hybrid mode, transactions generate composite signatures combining classical elliptic-curve signatures (ECDSA-P256 or Ed25519) with lattice-based post-quantum signatures. As quantum cryptanalysis advances, the System of Agreement updates the Policy Hash (PH) globally, directing KeyMESH to deprecate classical primitives and transition to pure PQC without requiring a single line of application code to be rewritten.
Native ML-KEM (Kyber) and ML-DSA (Dilithium) support safeguarding high-value transaction rails against store-now-decrypt-later adversaries.
Keys never exist in plaintext memory; operations execute inside AMD SEV-SNP enclaves with zero OS-level interception risk.
Every key rotation and signing assertion generates an immutable, non-repudiable audit event on the underlying ledger.
Deep Technical: Attested Nonce Injection & Merkle HyperDAG Leaf Randomisation
Deep Technical: Attested Nonce Injection & Merkle HyperDAG Leaf Randomisation
Within the Merkle HyperDAG architecture, a cryptographic nonce serves three foundational roles across the execution fabric: leaf-level salting, graph-level uniqueness, and commitment variation. KeyMESH operates as the authoritative entropy router, injecting hardware-attested nonces into every Minimum Viable Evidence Bundle (MVEB) without exposing raw secrets to the untrusted host operating system.
When hashing structured business logs or transaction payloads into leaf nodes, standard cryptographic hashes remain vulnerable to offline dictionary attacks if an observer can guess the format. KeyMESH concatenates an ephemeral, hardware-derived 256-bit nonce to each leaf payload before hashing. This randomises the leaf node, guaranteeing zero knowledge of underlying facts to any third party who observes intermediate Merkle proofs or authentication paths.
At the graph level, KeyMESH binds nonces to monotonic sequence counters rooted in the node's Hardware Bill of Materials (HBOM) and Write Once, Read Many (WORM) storage. This establishes temporal immutability and mathematically prevents replay attacks, ensuring that historical, valid evidence bundles cannot be repurposed by adversaries to authenticate duplicate state transitions across distributed mesh partitions.
Concatenated with raw evidence before hashing to guarantee absolute confidentiality against dictionary and rainbow table attacks.
Injected into DAG node relationships, binding state transitions to an unforgeable hardware-attested temporal coordinate.
Permits mutation of the top Merkle root commitment to emit time-varying signatures without rewriting underlying base data.
Deep Science: Multi-Party Computation & Threshold Mathematics
Deep Science: Multi-Party Computation & Threshold Mathematics
In a \((t, n)\) threshold secret-sharing scheme, a secret \(S \in \mathbb{F}_p\) is split among \(n\) participating nodes such that any subset of \(t\) nodes can reconstruct \(S\), whilst any group of \(t - 1\) or fewer nodes gains zero information regarding \(S\). KeyMESH constructs a random polynomial \(f(x)\) of degree \(t-1\) over the Galois Field \(\mathbb{F}_p\):
Each shard \(S_i = (i, f(i))\) is distributed to an isolated node. Given any subset of \(t\) shards \(\mathcal{S} \subset \{1, \dots, n\}\), the secret \(S = f(0)\) is recovered via Lagrange polynomial interpolation:
In threshold signing (e.g. threshold ECDSA/Schnorr), KeyMESH utilises homomorphic properties to generate valid cryptographic signatures across nodes without ever reconstructing the private key \(S\) on a single physical host, guaranteeing that no central honeypot exists in the execution pipeline.
Deep Science: Nonce Entropy, Bitemporal Posets & Hypergraph Commitments
Deep Science: Nonce Entropy, Bitemporal Posets & Hypergraph Commitments
Let \(\nu \in \{0,1\}^{256}\) denote a cryptographic nonce generated via a hardware True Random Number Generator (TRNG) satisfying entropy bound \(\mathbf{H}(\nu) \ge 256\). For each vertex \(v \in \mathcal{V}\) within a Lawful Act Hyperedge (LAHE), KeyMESH derives the leaf commitment \(H_v\) by binding the payload \(\mathbf{DBOM}(v)\), the attested nonce \(\nu_v\), and the bitemporal coordinate tuple \((T_V, T_X)\):
For an \(n\)-ary hyperedge \(e = \{v_1, v_2, \dots, v_k\}\), the overall HyperDAG commitment \(\mathcal{C}(e)\) is computed by aggregating vertex digests alongside a hyperedge sequence nonce \(\nu_e\) and the governing Policy Hash \(\mathcal{PH}\):
Because Valid Time (\(T_V\)) is anchored in attested sensor/TEE vectors whilst Transaction Time (\(T_X\)) is strictly monotonic, any retroactive state mutation inserts a delta pinned to \(T_V\) without mutating \(T_X\). The uniqueness guarantee of \(\nu_e\) ensures that collision probability \(\mathbb{P}(\mathcal{C}(e) = \mathcal{C}(e')) \le 2^{-256}\), rendering historical state rewriting mathematically impossible.
Post-Quantum Ephemeral Key Wrapping for Edge Compute Auctions & Offline Relief Custody
Under the STRM Axis 1 Crosswalk, KeyMESH (elem-comp-keymesh) provides the cryptographic root of ADR-R26 Safeguard S05 (Registrar + Notary + KeyMESH Triadic Custody Separation) using FIPS 140-3 Level 4 and ML-KEM-1024 / ML-DSA-87 post-quantum primitives. KeyMESH anchors both the CTC ⟷ RAH Edge AI Compute Spot Market (SEAM-2026-10-22-06) via ephemeral enclave workload keys and the NGO ⟷ PSL Disaster-Resilient Relief Seam (SEAM-2026-10-22-07) via threshold offline voucher signing.
The Substrate for Threshold: Why the Hard Part of Multi-Party Threshold Cryptography Is Deployment, and How onePOI.online Solves It
Grounded in the flagship position paper The Substrate for Threshold: onePOI.online and NIST IR 8214C, KeyMESH (elem-comp-keymesh, Ranked #11 Infomap Gatekeeper) positions the platform not as a proprietary mathematical primitive, but as the physical deployment substrate that open threshold schemes (NIST IR 8214C and RFC 9591 / FROST) require in the field.
Closing the 30-Year Deployment Gap
Threshold mathematics does not fail in the field; deployments do. NIST IR 8214C requires submitters to analyse security consequences when deployed outside idealised system models. KeyMESH and the multi-tenant POI Appliance solve the six field blockers: physical party isolation across separate silicon dies, hardware entropy sourcing, attested setup, coordinator constraint, Byzantine fault isolation, and offline partition survival.
RFC 9591 (FROST) & NIST IR 8214C
A constitutional authority layer that depends on a single vendor's closed primitive is not an authority layer at all. KeyMESH anchors on published, unpatented public standards (RFC 9591 two-round threshold Schnorr signatures and NIST IR 8214C open-source reference tracks) paired with ML-KEM-1024 and ML-DSA-87 post-quantum wrappers.
The End of the Key-Custody Argument
When signing authority is split across physically isolated silicon partitions inside the appliance and coordinated under DRAGON warrants, no single machine, administrator, cloud provider, or operator ever holds a usable key. The institution stops defending a policy control and presents a hardware-attested mathematical proof.
Together with Notary (Who Knew What, and When) and oneVault Mesh, KeyMESH enforces ADR-R26 Safeguard S05 (Triadic Custody Separation) across UK, EU, and MENAT sovereign deployments.